EN
 PT-BR
 FR
 ES
 DE

AI Summary
- SaaS companies can make changes that affect business operations. The blog describes an incident involving Office365/Microsoft 365 email forwarding to Freshdesk.
- Support addresses such as support@ and contact@ forwarded incoming messages to Freshdesk mailboxes, but no support tickets were raised for almost a week.
- Emails failed with “550 5.7.520 Access denied” because the organization did not allow external forwarding, following a security change in Office365/Microsoft365.
- The stated fix is to create an outbound policy in the Office 365 security and compliance portal, enable automatic forwarding, and apply it to selected support/contact senders.
- The same issue may occur with external customer support products including ZenDesk, Intercom, Help Scout, JIRA Service Desk, and Hubspot.
AI-generated content. It may contain errors.
See Document360 in action
One of the disadvantages of running your business on SaaS-based products is you never know the changes the SaaS companies make and the impact on your business.
Recently we had such an incident, we use Office365 / Microsoft 365 as our email provider and Freshdesk as our customer support platform. All the customer support emails like support@, contact@, etc are all configured to forward incoming emails to the corresponding Freshdesk configured mailboxes.
We noticed there were no support tickets raised for almost a week. When we logged in directly to the support mailbox, we saw a bunch of emails all failed with the following message
Delivery has failed to these recipients or groups:
Your message wasn’t delivered because the recipient’s email provider rejected it.
The message also contained a bit more detailed description
Remote Server returned ‘550 5.7.520 Access denied, Your organization does not allow external forwarding. Please contact your administrator for further assistance. AS(7555)’
This is due to a recent security change in Office365/Microsoft365. It makes sense to control the outbound /external email as an administrator. Since it increases significant risk if someone can get access to an email address.
How to fix this issue?
The fix is fairly straight forward.
- Login to Office 365 security and compliance portal (https://protection.office.com/antispam)
- Navigate to Threat Management > Policy (on the left-hand side)
- Click the button “Create an Outbound policy”
- Provide a friendly name (we called it “Freshdesk – allow forwarding policy”)
- Open the “Automatic forwarding” section and set “Automatic forwarding enabled” to “On – Forwarding is enabled”
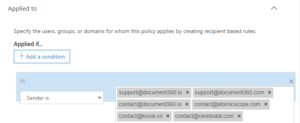
- Open the “Applied to” section and click on “Add a condition”
- Choose “Sender is” and on the RHS just select all the support/contact email addresses you wanted to forward. Our configuration looks like
We used Freshdesk, however, you’ll experience the same issue with any external customer support product like ZenDesk, Intercom, Help Scout, JIRA Service Desk, Hubspot etc